AI audit trail
AI arrived as a chat window and most logs still describe one. Every thread message, agent action and knowledge retrieval, recorded with the actor, the agent, its accountable manager, the model, the sources and the cost.
Free 25 users · $500 in credits · No credit card required
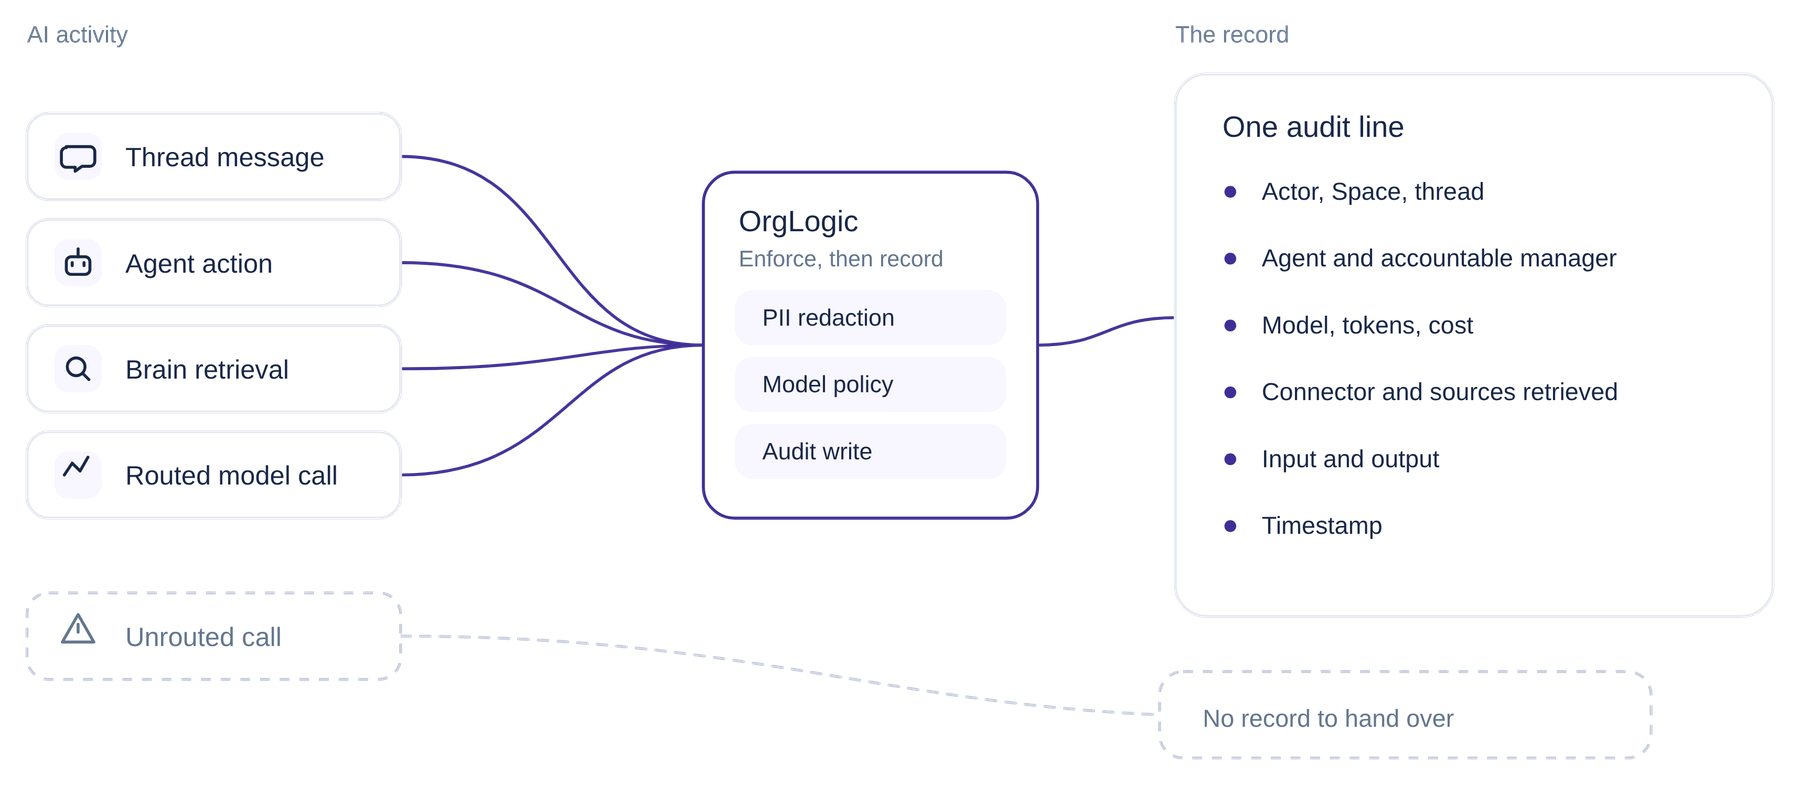
An AI audit trail is a durable record of what your AI did. Who asked, which agent acted, which model answered, which sources it drew on, what it returned and what it cost.
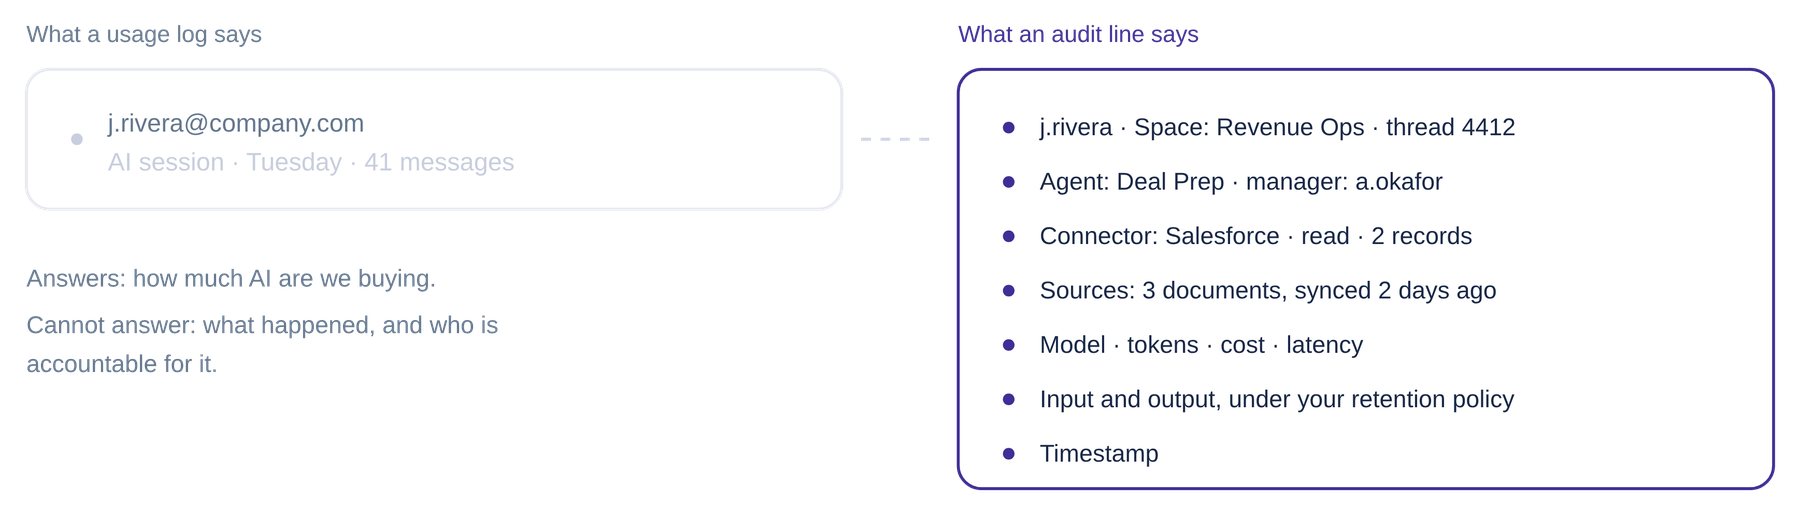
A usage report is the opposite, and it is what almost every company has today. Seats, messages, tokens. It tells you how much AI you are buying. It does not tell you what happened.
The distinction is not about how much data you keep. It is about the unit. In a usage report the unit is the session, so the best you can say is that somebody used AI on Tuesday. In an audit trail the unit is the action, so you can say which record was read, by which agent, for which person, on which model, from which sources.
The problem
This is what a session log costs, and the bill arrives in the week you need it. An agent read a customer record, drafted from a document nobody can name and posted the result into a ticket. Every part of that was recoverable at the time. None of it was recorded.
The shift
The unit
A session
An action
Who it names
An account, or an API key
The person, the agent, and the human accountable for the agent
What the AI reached
Not recorded
The connector accessed and the sources retrieved, with freshness
Which model answered
Sometimes
The model, and for routed calls the tokens, cost and latency
Your other AI tools
Out of scope
Routed through a gateway, with the same record
What you can do with it
Estimate adoption
Hand it to an auditor
Prevention
None, it reports
PII redacted before the model call, policy and caps at the call
Models commoditize. Every frontier lab is months from every other one. The record of what your company did with them does not commoditize, and it is the thing you will be asked to produce.
Requirements
Four things, and a chat history is only the first. A line per action, an accountable human behind every agent, the sources the answer was built from, and a record of the AI you did not buy from one vendor.
A session log tells you somebody used AI on Tuesday. An action log tells you which record was read, which ticket was updated and which document the answer came from. Regulators, auditors and your own incident reviews all work at the action level, and a line that resolves only to an API key tells you a system did something, which is the part you already knew.
An agent that runs on a schedule and writes to a connected system with nobody watching is a different problem from a person typing. The record has to name the agent, the connector it touched, and the human accountable for it. Autonomy without a named owner does not clear a security review.
Which documents the output was built from, and when they were last synced. Six months later, an answer you cannot trace to a source is an assertion, and nobody can defend an assertion in a review. Citations belong in the record, not only on the screen.
Your people run assistants you did not select and your teams build agents you did not commission. Routed through a gateway, those calls produce the same model, tokens, cost, latency and timestamp as everything else. Unrouted, they produce nothing, which is why routing comes before reporting.
Diagnosis
None of these come up often. All of them come up at the worst possible moment.
Which documents an AI answer was built from, six months after it was given.
Which agent touched a customer record, and who is accountable for that agent.
Whether a contract has ever been pasted into a chat window.
What your teams spend on AI, broken down by team, model and agent.
What the assistants you did not buy have been asked, and what they returned.
Whether an agent a departed employee configured is still running.
The EU AI Act requires high-risk AI systems to technically allow automatic recording of events over the lifetime of the system. Regulation (EU) 2024/1689. Verified 25 September 2026.
The minimum period deployers must keep those logs under Article 26(6). Obligations for Annex III systems apply from 2 December 2027 under Regulation (EU) 2026/1744. Verified 25 September 2026.
Controls
A record tells you what happened. AI model governance decides what is allowed to happen, and both have to sit in the same place or neither is enforceable.
Which models are available, set per organization and per team. New models do not arrive by default.
Your own provider keys at zero surcharge, so data flows directly to the provider and OrgLogic never sees it. Administrator configured.
Personal data auto-detected and masked before any prompt reaches a model, on every call from every Space and every agent.
Read or write per agent per connector, revocable in seconds, with a named manager accountable for every agent.
Spend by team, user, model and agent in real time, with alerts and hard caps that stop.
Two enforcement modes on the gateway. Observe is the default, so you see the traffic before you change anyone's day.
The obvious objection
No, and the difference decides whether the record is any use the day somebody asks for it. Exported chat history tells you what was typed. It does not tell you which agent acted on it, which system that agent reached, whose permissions it acted under, or which documents the answer was built from.
An AI audit trail means the action is the record. The agent is named and so is the human accountable for it. The connector and the sources are on the line. The model, the tokens and the cost are on the same line, so finance and security are reading the same evidence. And it extends to the assistants you did not buy, because their traffic runs through the same gateway.
A transcript you can download is a feature. A record you can hand to an auditor is a different product.
In practice
A pre-opening cognitive city development in Florida, fourteen districts, built by a confidential enterprise, put its master plans, designs and investor records in front of frontier models with zero confidential leaks, redacting 1.8M PII items in flight, with CISO sign-off in month one.
Two weeks matters more than it looks. Single-player tools roll out for months and still serve the same handful of power users, because every personAgent-level audit trails with a named manager accountable for every agent were the condition of the security review, not an outcome of it. Autonomous agents would never have cleared that review without per-agent permissions and a record of what each one did. has to discover their own value from scratch. When the value is already in the Space, the next member inherits it.
No confidential document has reached an ungoverned model endpoint since rollout.
Across finance, legal, procurement, investor relations and programme management.
Governance shipped as the first deliverable.
FAQ
A durable record of what your AI did: who asked, which agent acted, which model answered, which sources were used, what was returned and what it cost. The contrast is a usage report, which counts seats, messages and tokens and tells you how much AI you are buying rather than what happened.
Six things at minimum: the actor, the agent that acted and the human accountable for it, the model that answered, the connector or sources it reached, the input and output, and the timestamp and cost. OrgLogic writes all six on every thread message, agent action and knowledge retrieval that runs through it.
The record of what an autonomous agent did rather than what a person typed. Because an agent runs on a schedule or an event and acts in connected systems without anyone watching, the record has to name the agent, the connector it accessed and its manager. In OrgLogic every agent has a named manager whose ID is recorded on every audit line that agent produces.
The record of the model calls themselves: model, tokens, cost, latency, timestamp, input and output. In OrgLogic this comes from the AI Gateway, which is also the enforcement point for third-party AI clients and for agents your teams built on raw model APIs, so calls you did not originate produce the same record as the ones you did.
For high-risk systems, yes in substance. Article 12 requires high-risk AI systems to technically allow automatic recording of events over the lifetime of the system, and Article 26(6) requires deployers to keep those logs for at least six months. Regulation (EU) 2026/1744 moved obligations for stand-alone Annex III systems to 2 December 2027. Verified 25 September 2026. General information, not legal advice.
The set of controls that decide what your AI is allowed to do: which models are available to which teams, whose keys the traffic runs on, what is redacted before a prompt leaves, what content policies apply and what happens when a team hits a spend cap. Logging tells you what happened. Model governance decides what can.
Yes, for the model traffic you route through OrgLogic. Claude, ChatGPT, Copilot and Claude Code are supported clients when routed through the AI Gateway, and routed calls produce a record of agent, owner, model, tokens, cost, latency and timestamp. Retrievals those clients make from the Company Brain over MCP are logged separately with client, user, scope, sources and timestamp.
Private Space activity is logged like all other activity, and it is not shown in the in-app audit browser. Access is by compliance export under a role granted separately from Admin, and each export is itself audited.
Yes. Full audit trail, PII redaction, per-agent connector permissions, model availability controls and cost controls are on every plan including Free, for up to 25 users. SSO, SCIM, domain verification, single-tenant VPC and on-premise deployment sit on Enterprise, which carries a 100-seat minimum.
$0 up to 25 users, $8 per seat per month annually or $10 monthly on Standard, custom on Enterprise. Model usage separately: our keys at cost plus 6%, or your own at zero surcharge.
An AI workspace is a single environment where a whole company works with AI, instead of every team buying its own tool. One place to reach multiple models, answers grounded in the company's own documents and systems, and administrative control over what AI can see and do.
The phrase gets used for several different products, so the useful question is not what an AI workspace is in general. It is which kind you need.
Most tools that call themselves AI workspaces consolidate documents and tasks. An AI workspace built for a business consolidates something harder: models, knowledge, and control.
AI built into documents, task boards, and team chat. The AI drafts, summarizes, and automates inside the tools your team already uses to plan work.
Best when the problem is document and project overhead.

Environments where teams label and prepare training data for machine learning.
Best when you are building models, not using them.

One governed place for all AI use across a company. Multiple models, retrieval over internal knowledge, agents that act in business systems, and administrative controls over data, access, and spend.
Best when AI has spread across the company with no oversight. This is the category OrgLogic is in.
Hosted environments with the compute and tooling to develop and run AI models.
Best for data science and ML engineering teams who need infrastructure.

Use a consumer AI assistant. You need one model you like and a good interface. Governance, permissions, and per-seat economics are not your problem yet.
Look at a productivity workspace with AI built in. Your problem is coordination overhead, and the AI is there to reduce it.
The requirements change completely. People will want different models for different work. Answers have to come from company knowledge, not the public internet. IT and security need to see what AI is doing with company data. Finance needs the cost to survive a company-wide rollout.
Engineers, lawyers, and marketers do not want the same model. A business AI workspace gives access to every major model, lets people switch mid-conversation, and routes automatically to the right model for the task. One vendor's assistant can only ever offer one vendor's model. It should also govern the AI tools your teams already refuse to give up, rather than asking you to rip them out.
Not a feature you upgrade to. Bring your own API keys so data flows directly to model providers and OrgLogic never sees it. A full audit trail of every chat and agent action, searchable and exportable. PII redaction before anything reaches a model. Permissions set per agent, per connection, revocable in seconds.
Generic AI guesses about your business. A business AI workspace retrieves from your own documents and systems and cites the source document and how fresh it is, and tells you it does not know when retrieval comes back thin. An answer you cannot trace is an answer you cannot use.
AI tools priced at $25 to $60 a seat are affordable for a pilot team and painful at a thousand people. Model usage billed at cost, and a seat price that does not force you to ration access to the people who need it.
Every major model in one place. Switch models mid-conversation from a dropdown, or let smart routing pick the right one. Upload files for analysis, search the web with clickable citations, generate images, save prompts to a personal or shared library, and export any conversation to PDF or Markdown. Available on web, Slack, Microsoft Teams, and Chrome, so people use AI where they already work.
The grounded knowledge layer that Chat and Agents draw on inside OrgLogic. Knowledge bases hold uploaded files, websites, pasted text, and content pulled from connected systems, shared privately, with named people, or across the workspace. Personal knowledge syncs under each person's own credentials, so the index cannot contain anything they could not already access. Indexes refresh continuously, so answers reflect current state rather than the last sync, and every answer cites its source and when it was last synced.
AI workers built for a specific job and deployed to a team. Build one with a no-code builder, or start from a template for PR review, deal prep, ticket triage, contract review, onboarding questions, or policy lookup. Run them on demand, on a schedule, or triggered by an event like a new Jira ticket or a Salesforce stage change. Agents act in Salesforce, Jira, Confluence, ServiceNow, GitHub, SharePoint, Notion, Google Workspace, Slack, SAP, and any REST API. Every agent carries its own permissions and its own audit trail, so you can answer which agent accessed which record, for which user, at which time.
Default on every plan, including Free. BYOK at zero surcharge. Full audit trail across chat and agents. PII redaction applied before the model sees anything. Model availability controls per workspace and per team. Per-team budget controls with alerts and hard caps. Cost analytics by team, user, model, and agent. Configurable retention, complete isolation between workspaces, TLS 1.3 in transit, AES-256 at rest, and a contractual guarantee that customer data is never used for training.
Yes. OrgLogic is free for up to 25 users, with no seat minimum and no card required.
The Free plan is not a governance-free trial. BYOK, full audit trail, PII redaction, guardrails, per-agent permissions, cost analytics, and data retention controls are all included, along with the web app, Slack, Teams, and Chrome.
It also includes the part most teams assume is enterprise-only: the AI tools your people already use, including Claude, ChatGPT, and Copilot, can be routed through OrgLogic so their traffic inherits the same governance. You can see and control AI across your company before you have paid anything.
Every active user adds $20 to a shared credit pool for model usage, up to $500 at 25 users. Credits do not expire, and they carry over if you convert to a paid plan.
* One vendor's models
* $25 to $60 a seat
* Usage bundled, not itemized
* No bring-your-own keys
* Grounding limited to connected apps
* Cannot govern your other AI tools
* Usually one embedded model
* Bundled into the suite price
* Usage bundled, not itemized
* No bring-your-own keys
* Grounding limited to the suite's own content
* Cannot govern your other AI tools
* Every major model, switchable mid-chat, smart routing
* $8 a seat annual, $10 monthly
* BYOK at zero surcharge, or at cost plus 6%
* Bring your own keys on every plan
* Company Brain, with source and freshness on answers
* Governs Claude, ChatGPT, and Copilot through the gateway
* Free for 25 users, full governance included
Where does our data go?
With BYOK, you connect your own provider API keys and your data flows directly to the model providers. OrgLogic never sees it. Keys are configured by an administrator, so end users are never asked to bring their own. Nothing is used to train any model, contractually. Traffic is encrypted with TLS 1.3, storage with AES-256, and workspaces are completely isolated from one another.
What can we prove afterward?
Every chat and every agent action is logged, searchable, and exportable. Agent logs record which agent accessed which system objects, for which user, at which time. PII is detected and redacted before a prompt reaches a model, with the rules under your control. Retention is administrator-configurable.
A publicly traded autonomous vehicle technology company with roughly 1,500 employees consolidated 12 AI tools into OrgLogic, cut AI spend 70%, and reduced shadow AI by 91%, with engineers adopting within 2 weeks.
Their engineering teams had been running AI on personal accounts, with proprietary algorithms and sensor data going into tools nobody was tracking. BYOK kept that data inside their own environment. Smart routing let engineers pick the right model per task. Slack and Chrome drove the adoption.
Across Troopr Labs, the company behind OrgLogic, the platform runs in 600+ enterprise deployments, including Snowflake, Spotify, Rakuten, Snap, Delivery Hero, Wayfair, Aptean, and Cubic.
$0
Up to 25 users, no seat minimum. Full governance, including routing your existing AI tools through the gateway. $20 in model credits per active user, pooled, up to $500.
$8 per seat / month
Billed annually, or $10 monthly. Unlimited users, no seat minimum. Adds API and SDK access.
Custom
100 seat minimum. Adds SSO, SCIM, domain verification, single-tenant VPC, and on-premise deployment
An AI workspace is a single environment where a company works with AI instead of each team buying its own tool. It typically combines access to AI models, retrieval over the company's own documents and systems, and administrative control over data, access, and cost.
Is there a free AI workspace? / OrgLogic is free for up to 25 users with full governance included, no card required, and $20 of model credits per active user up to $500.
OrgLogic is free for up to 25 users with full governance included, no card required, and $20 of model credits per active user up to $500.
No. Google Workspace with Gemini embeds AI into Google's own productivity apps. A business AI workspace sits above your tools rather than inside one suite, gives access to models from multiple providers, and governs AI use across the company. Many OrgLogic customers use both, with Google Workspace connected as a source of company knowledge.
Those are single-vendor assistants: one provider's models, usage bundled into the seat price, typically $25 to $60 a seat. An AI workspace gives you every major model at $8 a seat with usage priced separately. You also do not have to choose. Claude, ChatGPT, Copilot, and Claude Code can be routed through OrgLogic on every plan, including Free, so they keep working while their model traffic inherits your governance.
In OrgLogic, permissions attach to connections and agents rather than to a single global setting. A person's own index is built under their own credentials, so it cannot contain anything they could not already access. Knowledge bases are shared privately, with named people, or workspace-wide. Each agent gets a read or write scope per connected system, and access can be revoked in seconds.
With BYOK, your data flows straight to the model providers and OrgLogic never sees it. PII is redacted before any prompt reaches a model, everything is logged and exportable, and OrgLogic is SOC 2 Type II and ISO 27001 certified, with HIPAA BAA and GDPR support. Enterprise adds single-tenant VPC and on-premise deployment.
OrgLogic is $0 up to 25 users, $8 per seat per month annually or $10 monthly on Standard, and custom on Enterprise. Model usage is billed separately: your own keys at zero surcharge, or OrgLogic-provisioned at cost plus 6%. Single-vendor assistants typically run $25 to $60 a seat with usage bundled and not itemized.
Yes, on every plan including Free, at zero surcharge. An administrator configures the keys once and data flows directly to the model providers. End users are never prompted to connect keys of their own.
A team can sign up and be working the same day. One publicly traded autonomous vehicle technology company with roughly 1,500 employees had engineers adopting within 2 weeks. Enterprise rollouts with SSO, SCIM, and a single-tenant deployment take longer and come with an implementation team.