Shadow AI solution for enterprises
Find the unsanctioned AI already running in your company, then remove the reason it exists. One governed workspace for every team, with the assistants they already use routed through it.
Free 25 users · Governance on every plan · No credit card required
Shadow AI detection is the practice of finding the AI tools, assistants and agents employees use for work without IT or security approval. The evidence already sits in your identity provider, your network logs, your expense data and your repositories, so a competent team can produce a first inventory in about a week.
The phrase covers two different jobs, so the useful question is not how to detect shadow AI. It is what you intend to do once you have the list.
Most shadow AI tools stop at the list. They tell you what people are using and leave you to block it, which moves the same work onto personal devices where nothing is visible at all. Shadow AI is a demand signal. Detection measures the demand. It does not serve it.
Why blocking does not hold ->Types
There are four, and they need different answers: consumer assistants on personal accounts, AI features switched on inside software you already bought, custom agents and scripts built on raw model APIs, and browser extensions on devices you do not manage.
Type 1
Free and personal-tier chat tools used for work, signed into with a personal email. The largest category by user count, and invisible the moment it happens on a phone.
Resolved by a sanctioned tool people prefer.
Type 2
Assistants and summarizers switched on inside tools procurement already approved. Nobody bought shadow AI, so nobody reviewed what the feature does with the data.
Resolved by an admin setting, once you know it is on.
Type 3
A team ships something against a model API with a key in a repository. It is now part of your production surface with no owner, no budget cap and no audit trail.
Resolved by registering the agent behind a gateway credential.
Type 4
Browser extensions with read access to every page, plus work done on personal phones and home laptops that no corporate control reaches.
Resolved by making the governed path the easier one.
Detection
Five sources, every one of them a system you already own. You do not need a new tool for the first pass, and working through them in this order gets you an inventory inside a week.
Pull third-party app consent records from your identity provider, Google Workspace and Microsoft 365. Every AI tool someone signed into with a corporate account left a grant behind, with a date and a scope. Sort by scope granted rather than by user count. One grant with broad mail or drive access matters more than fifty logins to a summarizer.
Query outbound traffic from managed devices to model provider API endpoints and consumer AI domains. Volume tells you how far adoption has spread. The endpoint tells you whether people are using finished products or calling APIs directly, which are different problems with different owners.
Filter card statements and expense reports for recurring charges under the approval threshold. Team subscriptions at $25 to $60 a seat rarely clear procurement, so they rarely appear in your vendor inventory or your renewal calendar.
Requirements
Five things: replace the tools people reached for, govern the ones they will not give up, log what happens, redact before the model sees anything, and cost something that survives a company-wide rollout.
Blocking a domain moves the work to a phone. The only durable fix is a sanctioned tool people prefer, which means every frontier model rather than one vendor's, switchable mid-thread, in the surfaces they already work in. This is the requirement most shadow AI tools skip, and it is the one that decides whether the number stays down after the first quarter.
Some of what you find is already load-bearing, and taking it away costs you the rollout. A shadow AI solution has to bring those tools inside rather than rip them out, so their model traffic inherits your model policy, your redaction rules and your budget caps while the people using them notice nothing.
A record of every message, agent action and retrieval, with the actor, the agent, its accountable manager, the model, the sources and the cost. Searchable and exportable, or it is not evidence. An inventory tells you what exists. A log tells you what happened.
Finding out afterwards does not un-send a customer list. Personal data has to be detected and masked before the prompt leaves your side, on every call, from every team and every agent, with the rules under your control rather than a vendor's.
Shadow AI is partly a pricing problem. At $25 to $60 a seat you ration access to whoever asks loudest, and everyone else goes back to a free tier on a personal account. A seat price that covers the whole company is a security control, not a procurement preference.
How OrgLogic works
Remove the reason shadow AI exists, bring the tools nobody will give up inside the perimeter, and turn both into a record you can hand to an auditor. On every plan including Free, with API and SDK from Standard.
Every frontier model in one place, switchable mid-thread, with smart routing per task. Teams work in shared Spaces where people and named agents post in the same threads, so one person's result is reusable by everybody. On web, Slack, Microsoft Teams and Chrome.
See Spaces ->
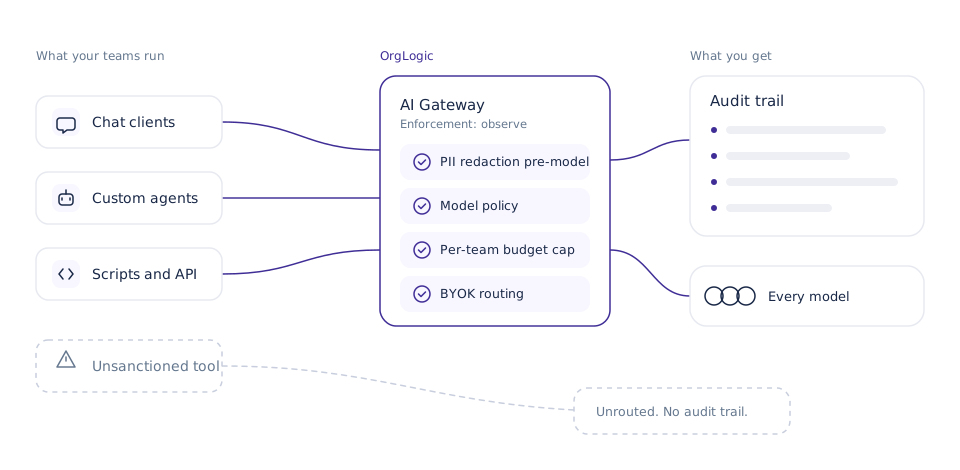
Claude, ChatGPT, Copilot and Claude Code are supported clients when routed through OrgLogic. Routed traffic inherits model availability controls, per-agent budget caps with hard stops, PII redaction and BYOK routing. Two enforcement modes, observe and block, with observe as the default.
See Governance ->
Every thread message, agent action and Brain retrieval logged with organization, Space, thread, actor, agent, accountable manager, model, sources and cost. That includes retrievals made from a third-party AI client. Searchable, exportable, with configurable retention.
Personal data auto-detected and masked before any prompt reaches a model, on every call from every Space and every agent. Bring your own provider keys at zero surcharge and data flows straight to the provider. Admin configured, so users are never prompted for keys.
Register every agent built outside OrgLogic with owner, team, framework, environment, version tag, access scope and status. One gateway credential per agent, revoked in one click, with call volume, cost and error rate per agent.
See AI Agents ->
Answers grounded in your own documents and systems, citing the source and when it was last synced, and saying it does not know when retrieval comes back thin. Connect it over MCP and the clients your teams already use answer from your knowledge too, scoped to each person.
See the Company Brain ->
Comparison

What it finds
Domains it has a rule for
Unsanctioned apps across the network, including tools that never touch OrgLogic
Every model call, agent action and retrieval routed through OrgLogic, plus the external agents you register
What happens next
The request is refused
A report you act on separately
The work continues, inside a governed workspace
Effect on the people using it
Work moves to personal devices
None, it observes
A tool most people prefer to the one they were using
Data exposure
Unchanged on anything not blocked
Unchanged, it reports rather than intervenes
PII redacted before the model call, BYOK so data goes straight to the provider
Evidence you can hand over
A block log
An inventory, accurate the day it is produced
A searchable, exportable record of every routed call, with the actor, agent and manager
Cost visibility
None
Sometimes, by application
Spend by team, user, model and agent, with alerts and hard caps
Your existing AI
Blocks it
Reports it
Governs its model traffic and grounds it in your knowledge over MCP
Security
It comes down to three things: whether your data trains anybody's model, whether sensitive data reaches the model at all, and whether you can prove afterwards what happened. A shadow AI solution should answer all three before you ask.
Nothing is used to train any model, contractually. Data sent to model providers goes by API only, is not retained beyond the time needed to answer, and every provider is under a DPA prohibiting use for training. Or bring your own keys at zero surcharge and it flows directly to the provider without OrgLogic seeing it. TLS 1.3 in transit, AES-256 at rest, complete isolation between organizations.
Personal data is detected and redacted before any prompt reaches a model, on every call from every Space and every agent, with the rules under your control. Guardrails and content policies are set at organization level, and model availability is set per organization and per team.
Every thread message, agent action and Brain retrieval is logged with the Space, thread, actor, agent, its accountable manager, model, sources and cost. That includes retrievals made from a third-party AI client. Searchable, exportable, with administrator-configurable retention.
SOC 2 Type II
ISO 27001
GDPR
HIPAA BAA
VPC and on-premise on Enterprise
In practice
A publicly traded autonomous vehicle technology company with roughly 1,500 employees consolidated 12 AI tools into OrgLogic, cut AI spend 70%, and reduced shadow AI by 91%, with engineers adopting within 2 weeks.
Their engineering teams had been running AI on personal accounts, with proprietary algorithms and sensor data going into tools nobody was tracking. BYOK kept that data inside their own environment. Smart routing let engineers pick the right model per task. Slack and Chrome drove the adoption.
Pricing
OrgLogic is $0 for up to 25 users, $8 per seat per month on annual billing or $10 monthly, and custom on Enterprise. Model usage is billed separately: our keys at cost plus 6%, or your own at zero surcharge. Single-vendor assistants typically run $25 to $60 a seat with usage bundled and not itemized.
Free
Up to 25 users, no seat minimum, no card.
Unlimited Spaces, threads and agents
Full governance
$500 in pooled model credits
Standard
seat / mo
Up to 25 users, no seat minimum, no card.
Everything in Free
API and SDK
Enterprise
100 seat minimum.
SSO, SCIM, domain verification
Single-tenant VPC and on-premise
FAQ
Shadow AI is the use of AI tools, assistants and agents for work without IT or security approval. It covers four kinds: consumer assistants on personal accounts, AI features switched on inside software the company already bought, custom agents and scripts built on raw model APIs, and browser extensions on devices nobody manages. IBM found 80% of employees use unsanctioned AI tools and puts the additional cost of a shadow AI breach at $670K (IBM, 2025).
The practice of finding that unapproved AI use and producing an inventory of it. The evidence usually already exists in identity provider consent records, network egress logs, expense data, browser extension inventories and API keys in repositories. Detection produces a list. It does not change what people do next, which is why detection alone does not hold.
Start with five sources you already own: third-party app consents in your identity provider, outbound traffic to model provider endpoints and consumer AI domains, recurring card charges below the procurement threshold, browser extensions with page-read permissions, and model provider API keys in repositories and CI. Then ask teams directly, with amnesty. The self-reported answer is faster than any scan and tells you what people actually needed.
They fall into three groups that do different jobs. Blocking and web filtering refuses the request. Discovery tools produce an inventory of unsanctioned applications across the network. A governed AI workspace gives the work somewhere sanctioned to go and logs it. The first two describe the problem, and only the third changes the behaviour that created it, so most organizations end up running a discovery pass alongside a governed workspace rather than choosing between them.
No. OrgLogic is not a network discovery tool. It governs the AI traffic that flows through it, which is why the approach is to make OrgLogic the tool people choose and route the assistants they already use through the gateway. Once traffic runs through OrgLogic you get a full audit trail, per-agent observability, a registry of externally built agents, and cost analytics by team, user, model and agent.
You can, and blocking alone tends to push the same work onto personal devices where there is no visibility at all. The OrgLogic gateway supports two enforcement modes, observe and block, with observe as the default, because seeing the traffic is worth more than stopping it on day one.
No. Claude, ChatGPT, Copilot and Claude Code are supported clients when routed through OrgLogic, on every plan including Free. Their model traffic inherits your model policy, PII redaction, budget caps and audit trail. Separately, the Company Brain is callable over MCP, so those clients answer from your own accounts and documents, serving each person only what they were already entitled to.
No, and it is a contractual guarantee. Data sent to model providers goes by API only, is not retained beyond the time needed to generate a response, and every provider is under a DPA prohibiting use for training. This applies to OrgLogic-provisioned models and to BYOK alike.
No. BYOK, PII redaction pre-model, full audit trail, per-agent connector permissions, model availability controls and cost controls are on every plan including Free. SSO, SCIM, domain verification, single-tenant VPC and on-premise deployment sit on Enterprise, which carries a 100-seat minimum.
OrgLogic is $0 up to 25 users, $8 per seat per month annually or $10 monthly on Standard, and custom on Enterprise. Model usage is billed separately: your own keys at zero surcharge, or OrgLogic-provisioned at cost plus 6% on prepaid credits. Single-vendor assistants typically run $25 to $60 a seat with usage bundled and not itemized.
A team can sign up and be working the same day. One publicly traded autonomous vehicle technology company with roughly 1,500 employees had engineers adopting within 2 weeks. Enterprise rollouts with SSO, SCIM and a single-tenant deployment take longer and come with an implementation team.
An AI workspace is a single environment where a whole company works with AI, instead of every team buying its own tool. One place to reach multiple models, answers grounded in the company's own documents and systems, and administrative control over what AI can see and do.
The phrase gets used for several different products, so the useful question is not what an AI workspace is in general. It is which kind you need.
Most tools that call themselves AI workspaces consolidate documents and tasks. An AI workspace built for a business consolidates something harder: models, knowledge, and control.
AI built into documents, task boards, and team chat. The AI drafts, summarizes, and automates inside the tools your team already uses to plan work.
Best when the problem is document and project overhead.

Environments where teams label and prepare training data for machine learning.
Best when you are building models, not using them.

One governed place for all AI use across a company. Multiple models, retrieval over internal knowledge, agents that act in business systems, and administrative controls over data, access, and spend.
Best when AI has spread across the company with no oversight. This is the category OrgLogic is in.
Hosted environments with the compute and tooling to develop and run AI models.
Best for data science and ML engineering teams who need infrastructure.

Use a consumer AI assistant. You need one model you like and a good interface. Governance, permissions, and per-seat economics are not your problem yet.
Look at a productivity workspace with AI built in. Your problem is coordination overhead, and the AI is there to reduce it.
The requirements change completely. People will want different models for different work. Answers have to come from company knowledge, not the public internet. IT and security need to see what AI is doing with company data. Finance needs the cost to survive a company-wide rollout.
Engineers, lawyers, and marketers do not want the same model. A business AI workspace gives access to every major model, lets people switch mid-conversation, and routes automatically to the right model for the task. One vendor's assistant can only ever offer one vendor's model. It should also govern the AI tools your teams already refuse to give up, rather than asking you to rip them out.
Not a feature you upgrade to. Bring your own API keys so data flows directly to model providers and OrgLogic never sees it. A full audit trail of every chat and agent action, searchable and exportable. PII redaction before anything reaches a model. Permissions set per agent, per connection, revocable in seconds.
Generic AI guesses about your business. A business AI workspace retrieves from your own documents and systems and cites the source document and how fresh it is, and tells you it does not know when retrieval comes back thin. An answer you cannot trace is an answer you cannot use.
AI tools priced at $25 to $60 a seat are affordable for a pilot team and painful at a thousand people. Model usage billed at cost, and a seat price that does not force you to ration access to the people who need it.
Every major model in one place. Switch models mid-conversation from a dropdown, or let smart routing pick the right one. Upload files for analysis, search the web with clickable citations, generate images, save prompts to a personal or shared library, and export any conversation to PDF or Markdown. Available on web, Slack, Microsoft Teams, and Chrome, so people use AI where they already work.
The grounded knowledge layer that Chat and Agents draw on inside OrgLogic. Knowledge bases hold uploaded files, websites, pasted text, and content pulled from connected systems, shared privately, with named people, or across the workspace. Personal knowledge syncs under each person's own credentials, so the index cannot contain anything they could not already access. Indexes refresh continuously, so answers reflect current state rather than the last sync, and every answer cites its source and when it was last synced.
AI workers built for a specific job and deployed to a team. Build one with a no-code builder, or start from a template for PR review, deal prep, ticket triage, contract review, onboarding questions, or policy lookup. Run them on demand, on a schedule, or triggered by an event like a new Jira ticket or a Salesforce stage change. Agents act in Salesforce, Jira, Confluence, ServiceNow, GitHub, SharePoint, Notion, Google Workspace, Slack, SAP, and any REST API. Every agent carries its own permissions and its own audit trail, so you can answer which agent accessed which record, for which user, at which time.
Default on every plan, including Free. BYOK at zero surcharge. Full audit trail across chat and agents. PII redaction applied before the model sees anything. Model availability controls per workspace and per team. Per-team budget controls with alerts and hard caps. Cost analytics by team, user, model, and agent. Configurable retention, complete isolation between workspaces, TLS 1.3 in transit, AES-256 at rest, and a contractual guarantee that customer data is never used for training.
Yes. OrgLogic is free for up to 25 users, with no seat minimum and no card required.
The Free plan is not a governance-free trial. BYOK, full audit trail, PII redaction, guardrails, per-agent permissions, cost analytics, and data retention controls are all included, along with the web app, Slack, Teams, and Chrome.
It also includes the part most teams assume is enterprise-only: the AI tools your people already use, including Claude, ChatGPT, and Copilot, can be routed through OrgLogic so their traffic inherits the same governance. You can see and control AI across your company before you have paid anything.
Every active user adds $20 to a shared credit pool for model usage, up to $500 at 25 users. Credits do not expire, and they carry over if you convert to a paid plan.
* One vendor's models
* $25 to $60 a seat
* Usage bundled, not itemized
* No bring-your-own keys
* Grounding limited to connected apps
* Cannot govern your other AI tools
* Usually one embedded model
* Bundled into the suite price
* Usage bundled, not itemized
* No bring-your-own keys
* Grounding limited to the suite's own content
* Cannot govern your other AI tools
* Every major model, switchable mid-chat, smart routing
* $8 a seat annual, $10 monthly
* BYOK at zero surcharge, or at cost plus 6%
* Bring your own keys on every plan
* Company Brain, with source and freshness on answers
* Governs Claude, ChatGPT, and Copilot through the gateway
* Free for 25 users, full governance included
Where does our data go?
With BYOK, you connect your own provider API keys and your data flows directly to the model providers. OrgLogic never sees it. Keys are configured by an administrator, so end users are never asked to bring their own. Nothing is used to train any model, contractually. Traffic is encrypted with TLS 1.3, storage with AES-256, and workspaces are completely isolated from one another.
What can we prove afterward?
Every chat and every agent action is logged, searchable, and exportable. Agent logs record which agent accessed which system objects, for which user, at which time. PII is detected and redacted before a prompt reaches a model, with the rules under your control. Retention is administrator-configurable.
A publicly traded autonomous vehicle technology company with roughly 1,500 employees consolidated 12 AI tools into OrgLogic, cut AI spend 70%, and reduced shadow AI by 91%, with engineers adopting within 2 weeks.
Their engineering teams had been running AI on personal accounts, with proprietary algorithms and sensor data going into tools nobody was tracking. BYOK kept that data inside their own environment. Smart routing let engineers pick the right model per task. Slack and Chrome drove the adoption.
Across Troopr Labs, the company behind OrgLogic, the platform runs in 600+ enterprise deployments, including Snowflake, Spotify, Rakuten, Snap, Delivery Hero, Wayfair, Aptean, and Cubic.
$0
Up to 25 users, no seat minimum. Full governance, including routing your existing AI tools through the gateway. $20 in model credits per active user, pooled, up to $500.
$8 per seat / month
Billed annually, or $10 monthly. Unlimited users, no seat minimum. Adds API and SDK access.
Custom
100 seat minimum. Adds SSO, SCIM, domain verification, single-tenant VPC, and on-premise deployment
An AI workspace is a single environment where a company works with AI instead of each team buying its own tool. It typically combines access to AI models, retrieval over the company's own documents and systems, and administrative control over data, access, and cost.
Is there a free AI workspace? / OrgLogic is free for up to 25 users with full governance included, no card required, and $20 of model credits per active user up to $500.
OrgLogic is free for up to 25 users with full governance included, no card required, and $20 of model credits per active user up to $500.
No. Google Workspace with Gemini embeds AI into Google's own productivity apps. A business AI workspace sits above your tools rather than inside one suite, gives access to models from multiple providers, and governs AI use across the company. Many OrgLogic customers use both, with Google Workspace connected as a source of company knowledge.
Those are single-vendor assistants: one provider's models, usage bundled into the seat price, typically $25 to $60 a seat. An AI workspace gives you every major model at $8 a seat with usage priced separately. You also do not have to choose. Claude, ChatGPT, Copilot, and Claude Code can be routed through OrgLogic on every plan, including Free, so they keep working while their model traffic inherits your governance.
In OrgLogic, permissions attach to connections and agents rather than to a single global setting. A person's own index is built under their own credentials, so it cannot contain anything they could not already access. Knowledge bases are shared privately, with named people, or workspace-wide. Each agent gets a read or write scope per connected system, and access can be revoked in seconds.
With BYOK, your data flows straight to the model providers and OrgLogic never sees it. PII is redacted before any prompt reaches a model, everything is logged and exportable, and OrgLogic is SOC 2 Type II and ISO 27001 certified, with HIPAA BAA and GDPR support. Enterprise adds single-tenant VPC and on-premise deployment.
OrgLogic is $0 up to 25 users, $8 per seat per month annually or $10 monthly on Standard, and custom on Enterprise. Model usage is billed separately: your own keys at zero surcharge, or OrgLogic-provisioned at cost plus 6%. Single-vendor assistants typically run $25 to $60 a seat with usage bundled and not itemized.
Yes, on every plan including Free, at zero surcharge. An administrator configures the keys once and data flows directly to the model providers. End users are never prompted to connect keys of their own.
A team can sign up and be working the same day. One publicly traded autonomous vehicle technology company with roughly 1,500 employees had engineers adopting within 2 weeks. Enterprise rollouts with SSO, SCIM, and a single-tenant deployment take longer and come with an implementation team.